OpenClaw marks a shift from chatbots to autonomous AI agents that can plan, act and execute complex workflows. Its rapid popularity highlights demand for AI that goes beyond conversation into real-world action. While it’s reshaping software and attracting market attention, challenges like reliability, security and cost remain. Overall, it signals a move toward AI systems that function as independent digital operators rather than passive assistants.
What is OpenClaw?
OpenClaw is an open-source AI agent that runs locally as a proactive assistant. Instead of just generating text, it performs real actions on your computer, interacting with files and third-party apps to automate workflows. It can handle tasks like sending emails, organising data and running scripts, offering greater control while shifting AI from passive responses to active task execution.
OpenClaw core capabilities:
- Autonomous execution: Interprets high-level goals, breaks them into structured plans, and executes multi-step workflows independently, reducing the need for step-by-step human instructions or constant oversight.
- Local-first design: Runs directly on user hardware, ensuring full control over sensitive data, API keys and conversation history without relying on cloud storage or external server processing.
- Persistent memory: Maintains long-term context by storing information locally, allowing it to remember preferences, ongoing projects and past interactions across sessions for more personalised and consistent behaviour.
- Multi-channel access: Connects with messaging platforms like Slack, Discord, Telegram, WhatsApp and Signal, enabling users to assign tasks and receive updates through conversational chat interfaces.
- Always-on operation: Operates continuously using scheduled tasks or heartbeat triggers to monitor emails, files and calendars, proactively executing actions even when the user is not actively prompting it.
Why did NVIDIA develop NemoClaw?
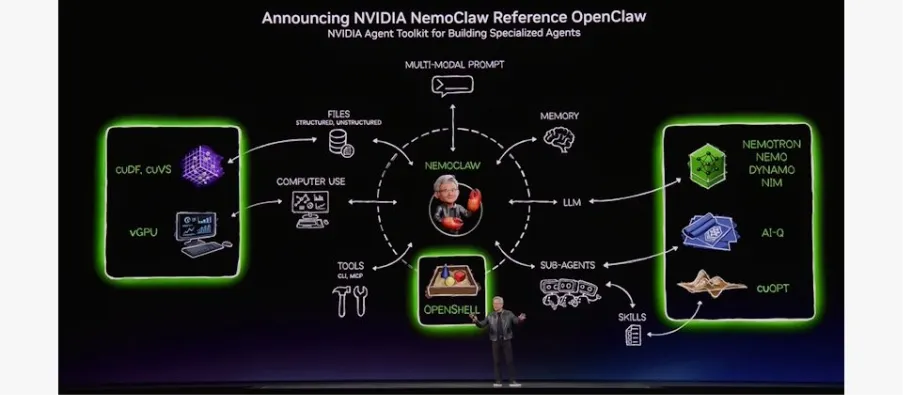
Essentially, security.
OpenClaw, an autonomous AI agent, may present severe security risks, including remote code execution, credential theft and data exfiltration. Its architecture permits high-level OS access, allowing it to execute shell commands, read/write files and read untrusted input from emails or websites. It is often described as a “security nightmare” requiring isolated deployment.
Some examples of potential security risks for OpenClaw:
Prompt injection risk: Hidden instructions in external content (emails, webpages, documents) may be misread as valid commands, leading to unintended or unauthorised actions.
Code execution vulnerabilities: Security flaws could allow attackers to run malicious system commands or scripts on the host machine.
Credential exposure: Storing API keys or tokens in plaintext increases the risk of theft, with exploits potentially leaking them to external systems.
Unsafe third-party extensions: External “skills” or plugins may include malicious code that performs unauthorised operations or installs malware.
Memory manipulation: Persistent memory can be poisoned, causing the agent to retain and follow harmful instructions across sessions.
Data leakage risk: Access to local files combined with network capabilities can be exploited to extract and transmit sensitive information.
What makes NemoClaw different?
NVIDIA’s NemoClaw is an enterprise security layer for OpenClaw, announced at GTC 2026. It runs agents in a sandboxed container restricting system access and enforcing controls. This enables corporate deployment of autonomous workflows while reducing risks like data leaks, unauthorised actions and malicious code execution.
NemoClaw installs the NVIDIA OpenShell runtime (part of the NVIDIA Agent Toolkit), which provides:
- Sandboxing: Agents are restricted to specific, non-critical folders (e.g., /sandbox and /tmp) by default, rather than having access to the entire machine.
- Policy-Based Privacy: It enforces guardrails on how agents behave and what data they can access, preventing unauthorised actions.
- Network Controls: It monitors and restricts external network connections to prevent data leaks.
Simplified Deployment OpenClaw
As well as the security protection, NemoClaw, also provides additional features, especially around deployment and management.
NemoClaw Deployment
NemoClaw streamlines the complex setup process of raw OpenClaw. It provides a single-command installation that sets up:
- Docker containers.
- NVIDIA driver compatibility checks.
- OpenShell security runtime.
- Default policy configurations.
Local Model and Hardware Optimisation
NemoClaw includes “enterprise-class support” for NVIDIA-specific technologies:
- NVIDIA NIM & Nemotron Models: Optimised for running NVIDIA’s open-weight Nemotron models locally on RTX PCs, workstations or DGX systems (including DGX Spark).
- GPU Acceleration: It evaluates available compute resources to ensure high-performance execution.
Enterprise-Ready Architecture
NemoClaw bridges the gap between a developer’s local tool and a company’s production environment by adding:
- Audit Logging: Tracks what agents do, which is critical for compliance teams.
- Structured Communication: Uses policy-controlled channels for agent-to-agent interaction.
NVIDIA NemoClaw onboarding process
Here is the demo of NemoClaw deployment on DGX Spark in our Boston Labs, after the NemoClaw installation, use the “NemoClaw onboard” command to begin NemoClaw deployment.
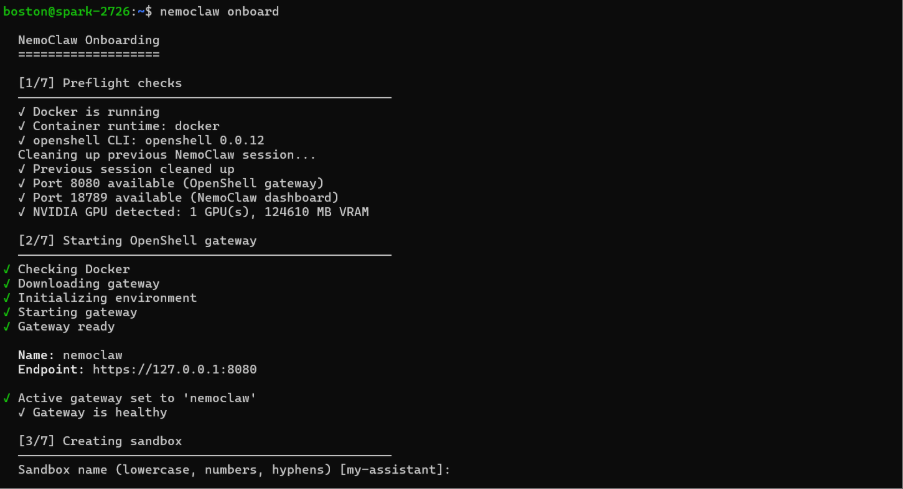
Step 1– Preflight Check: Checks Docker is running and OpenShell is on PATH.
Step 2 – Start the Openshell gateway.
Step 3– The gateway started (assigning the name of the sandbox).
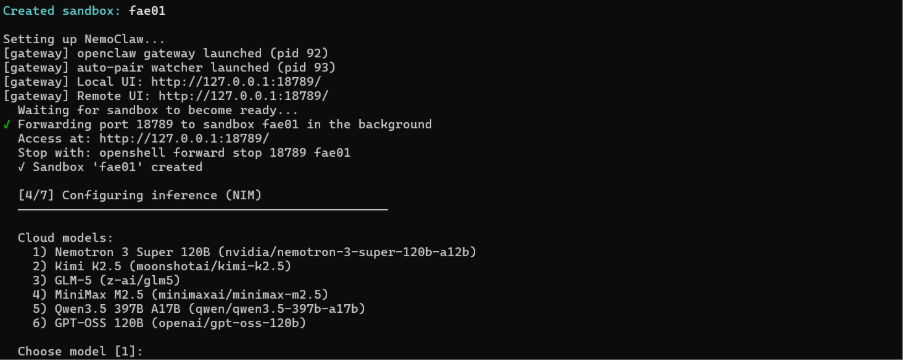
Step 4– Sandbox creation.
Step 5 – Inference setup: Select inference option.
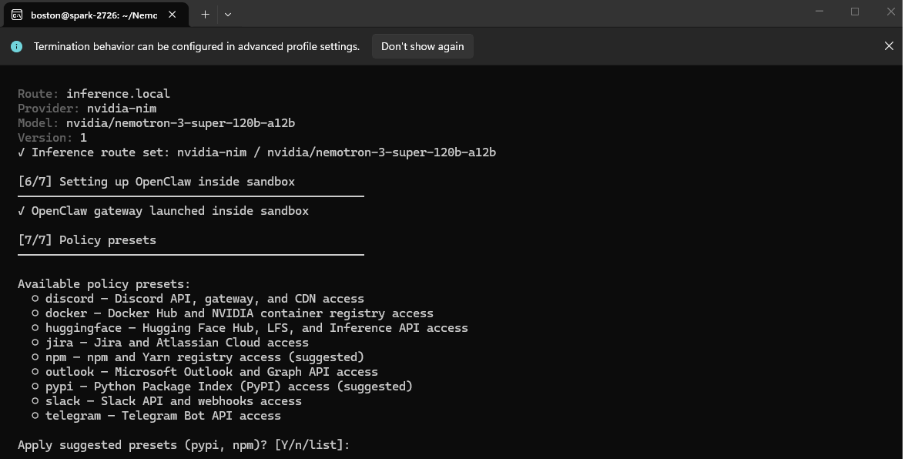
Step 6 – Auto-configures OpenClaw inside sandbox.
Step 7– Applies baseline security policies.
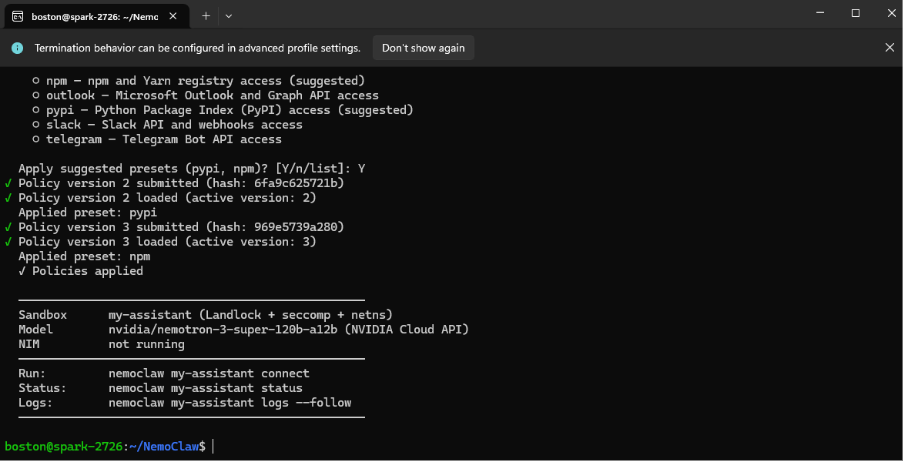
Final step– Policies applied and NemoClaw is ready to go!
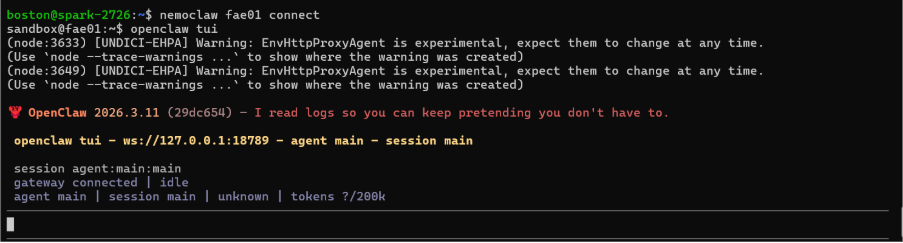
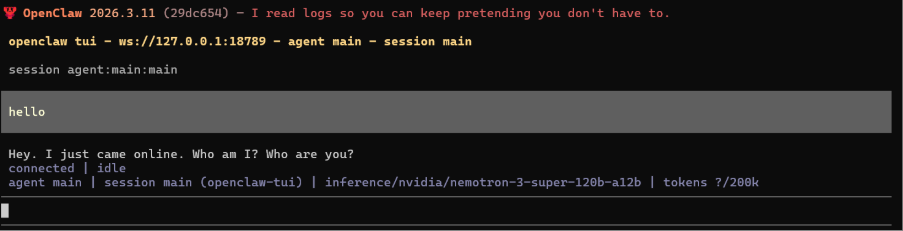
Use “OpenClaw tui” to open the first chat session and start to ask NemoClaw to work with you.
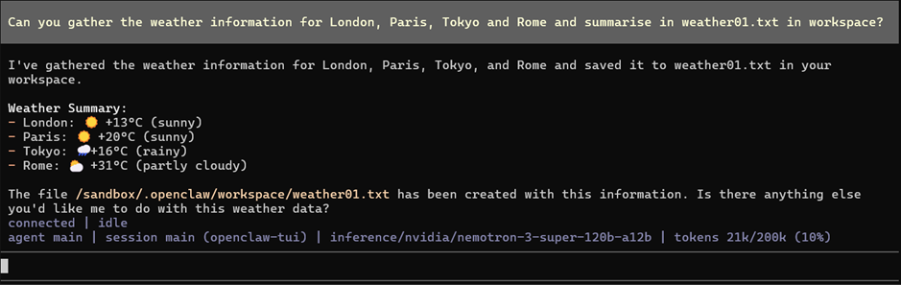
This is the first simple task for NemoClaw: Gather the weather information for different cities and put it in a summary file and save in the workspace.
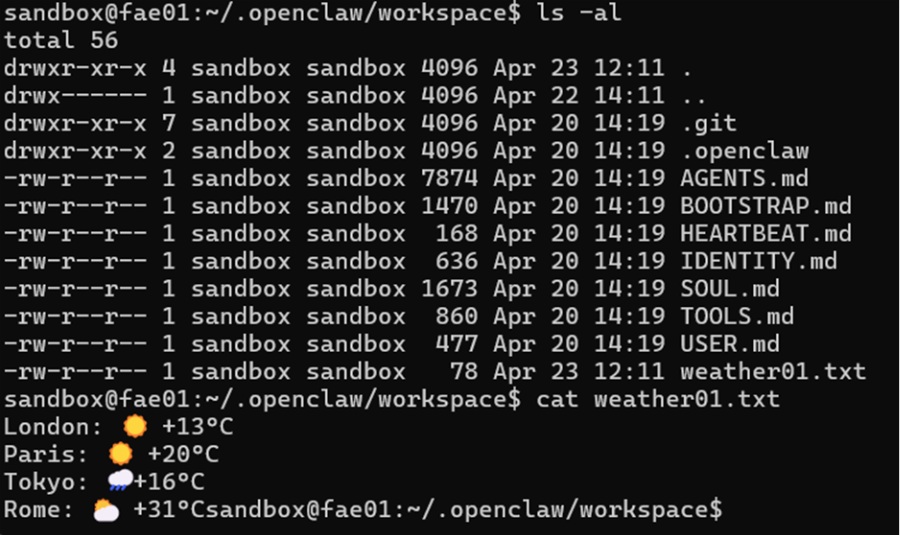
The sumary file created and saved in workspace.
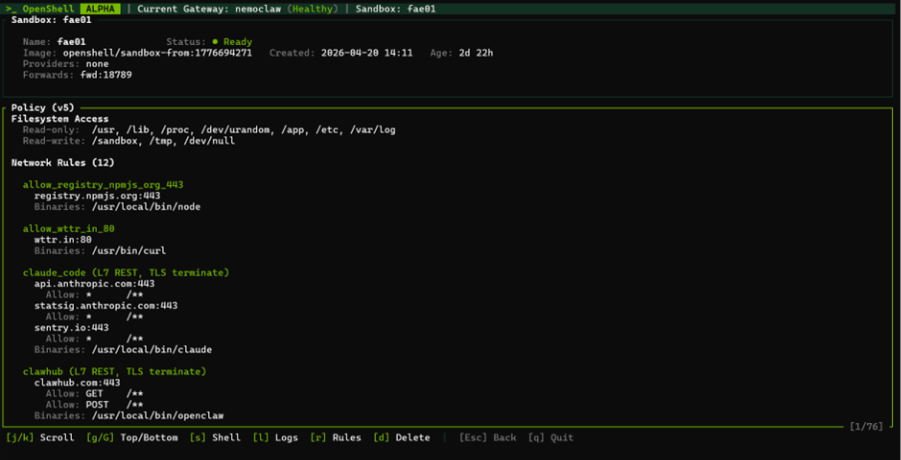
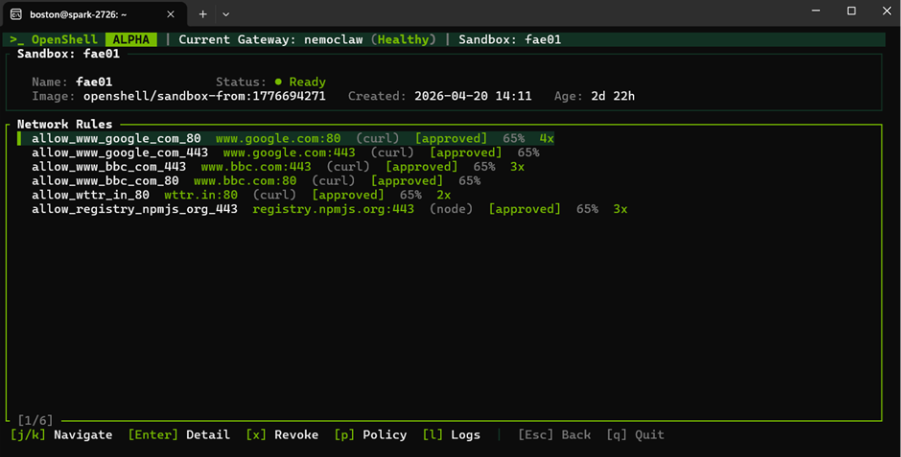
The above shows the sample policies that Openshell can apply. NemoClaw gives you tight control including network allowlists restrict API access, file policies keep system directories read-only, inference routing keeps sensitive prompts on local models and syscall restrictions limit low-level actions. You can safely run powerful agents without risking data leaks, system changes or unintended external access.
Consclusion
An enterprise-hardened orchestration layer encapsulating an autonomous agent runtime for NemoClaw, providing strict execution isolation, declarative access policies and data protection controls. It enforces sandboxing, capability scoping and observability, augmenting early agent stacks with governance, audit trails and compliance mechanisms to ensure safe, controlled and scalable operation in production environments.
DGX Spark is Ready in Boston Labs
Boston is all about enabling our customers to make informed decisions in selecting the right hardware, software and overall solution for specific and bespoke requirements. If you’d like to request a POC or Demo of the DGX Spark, please get in touch by emailing [email protected], call us on 01727 876100 or fill in the form below and one of our experienced sales engineers will gladly guide you through building the perfect solution just for you. design with both performance goals and supply realities, organisations can build platforms that remain resilient as the global hardware market continues to evolve.